# Feature - SAML (planned for r46)
**URL:** https://discussions.eramba.org/t/feature-saml-planned-for-r46/494
**Category:** Forum - Software
**Created:** [November 14, 2017, 10:43am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494 "2017-11-14T10:43:20Z")
**Posts on this page:** 20
**Page:** 1
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [November 14, 2017, 10:43am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/1 "2017-11-14T10:43:20Z")
We need to let people authenticate with one more mechanism (on top of LDAP and local accounts): SAML
Under System / Settings we need a new option for “SAML Connectors”
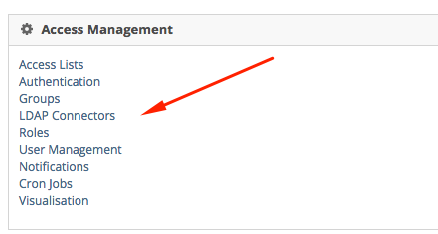
When clicked there, the user can define one or more SAML connectors.
At System / Settings / Authentication we need to allow SAML authentication for: General Eramba Authentication (we will include later one Third Party Audits Portal Authentication).
Warning: user management will be handled as usual, local accounts must exist for SAML to authenticate. This issue goes back to [Feature - Enabling two factor auth (no due date)](https://discussions.eramba.org/t/enabling-two-factor-auth/119) by @mitchell_e_rowton and @ksaxena
[https://github.com/eramba/eramba\_v2/issues/459](https://github.com/eramba/eramba_v2/issues/459)
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [December 1, 2017, 11:49am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/2 "2017-12-01T11:49:52Z")
Due a set of dependencies we have worked out Oauth authentication:
[ ](https://www.youtube.com/watch?v=aeH8BI84YCo)
In order to work with SAML we need a testing SSO enviroment to work with, those of you that requested SAML can work with oauth too or need SAML?
Regards
---
### Author:  [@bfailla](https://discussions.eramba.org/u/bfailla)
#### Post date: [January 23, 2018, 5:17pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/3 "2018-01-23T17:17:10Z")
Is there an update on SAML? We’re interested. It says planned for R46, but I don’t see it.
---
### Author:  [@ef1](https://discussions.eramba.org/u/ef1)
#### Post date: [January 24, 2018, 12:32pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/4 "2018-01-24T12:32:55Z")
Hi!
We implemented a beta version of Google oauth in release 47. You Can find more details in the video posted in the release note : [http://www.eramba.org/enterprise-update-47/](http://www.eramba.org/enterprise-update-47/)
Let us know what do you think!
Thanks!
---
### Author:  [@bjoern.rudner](https://discussions.eramba.org/u/bjoern.rudner)
#### Post date: [April 11, 2018, 9:28am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/5 "2018-04-11T09:28:26Z")
I’m also very interested in using SAML as Login with our sso solution.
Are there any future plans on implementing SAML or other OAuth-Providers.
Our Company is using an IAM solution by NetIQ.
I can also provide the ability to testdrive some configurations.
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [April 12, 2018, 4:55pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/6 "2018-04-12T16:55:21Z")
I’m not %100 sure about SAML, oauth is for sure going to be expanded to other providers (or custom providers) but not until we complete UX migration (a couple of months if we get lucky).
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [April 16, 2019, 9:38am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/7 "2019-04-16T09:38:07Z")
hello,
we will be working on saml on the next two releases , we dont have experience on the technology so it would be good if we can collaborate with a couple of customers that:
- have build saml server (so we understand deeper how the technology works)
- have configured an application to work with saml (so we know how ux, settings, etc would work)
both is ideal, one of them is really good too.
our plan is to expand authentication (not authorisation) to saml but we would still require local accounts in eramba to be created. this will take a month or two but hopefully we can start to collect the information we need to plan on how to build it.
please contact [support@eramba.org](mailto:support@eramba.org) if you are able to help
regards,
esteban
---
### Author:  [@pedro.goncalves](https://discussions.eramba.org/u/pedro.goncalves)
#### Post date: [May 13, 2019, 8:16am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/8 "2019-05-13T08:16:20Z")
We also are interested in SAML (i.e. authorisation) through OKTA. Maybe you could do some tests with us.
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [July 9, 2019, 11:44am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/9 "2019-07-09T11:44:28Z")
We have almost confirmed funding from one of our customers to implement SAML 2.0 , we would appreciate if those of you that have applications using SAML 2.0 to send us over screesnhots that show what configuration parameters they use so we make sure we build something that will work more or less the same way your other SAML compatible apps
---
### Author:  [@pedro.goncalves](https://discussions.eramba.org/u/pedro.goncalves)
#### Post date: [July 9, 2019, 12:45pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/10 "2019-07-09T12:45:56Z")
Hi,
We use Okta as our identity service. Here is their step by step to integrate SAML 2.0 applications (including fields needed).
[https://developer.okta.com/docs/guides/saml-application-setup/overview/](https://developer.okta.com/docs/guides/saml-application-setup/overview/)
---
### Author:  [@matthew.dovie](https://discussions.eramba.org/u/matthew.dovie)
#### Post date: [July 9, 2019, 12:55pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/11 "2019-07-09T12:55:59Z")
Similar to how you’re syncing LDAP accounts to local accounts, you would be able to use Just-in-Time provisioning to create local accounts through SAML. Instead of syncing users from an Active Directory instance, with Just-in-Time provisioning users are created and updated dynamically when they log in, based on SAML assertions sent by the identity provider.
---
### Author:  [@phillip\_rice](https://discussions.eramba.org/u/phillip_rice)
#### Post date: [July 12, 2019, 11:37am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/12 "2019-07-12T11:37:22Z")
> [@blair.charleville](#):
>
> Just-in-Time provisioning
This would be a massive benefit - a default group be set if no group info is passed, or if group info is passed and matches an existng group in eramba then the user would be set as a member of the group 🙂
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [July 15, 2019, 6:39am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/13 "2019-07-15T06:39:17Z")
We were thinking on using SAML only to authenticate users, the eramba user must be previously created (trough imports or ldap sync) before you can authenticate it !
---
### Author:  [@phillip\_rice](https://discussions.eramba.org/u/phillip_rice)
#### Post date: [July 15, 2019, 8:30am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/14 "2019-07-15T08:30:04Z")
Think on using or decided? 🙂
---
### Author:  [@phillip\_rice](https://discussions.eramba.org/u/phillip_rice)
#### Post date: [July 16, 2019, 9:04am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/15 "2019-07-16T09:04:37Z")
If just in time provisioning is still a possibility please let me know, if not I will have to consider alternatives as we cannot connect Eramba to our ldap directory.
Thanks
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [July 16, 2019, 9:29am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/16 "2019-07-16T09:29:11Z")
hello,
saml 2.0 will be used as another authentication method alone not used for syncing accounts to eramba, for that we use ldap.
sorry!
---
### Author:  [@pedro.goncalves](https://discussions.eramba.org/u/pedro.goncalves)
#### Post date: [August 12, 2019, 2:35pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/17 "2019-08-12T14:35:04Z")
Can you put on the pipeline provisioning (even if is not in the near future) ? I guess that’s the major factor to use SAML instead of LDAP or Oauth which you already support.
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [August 14, 2019, 2:17pm UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/18 "2019-08-14T14:17:20Z")
For the time being we need to keep this as it is … sorry but we have too many fronts and we need to choose battles carefully !
---
### Author:  [@pedro.goncalves](https://discussions.eramba.org/u/pedro.goncalves)
#### Post date: [August 16, 2019, 7:40am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/19 "2019-08-16T07:40:18Z")
Yes, Understandable 😉
---
### Author:  [@eramba](https://discussions.eramba.org/u/eramba)
#### Post date: [September 24, 2019, 7:27am UTC](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494/20 "2019-09-24T07:27:03Z")
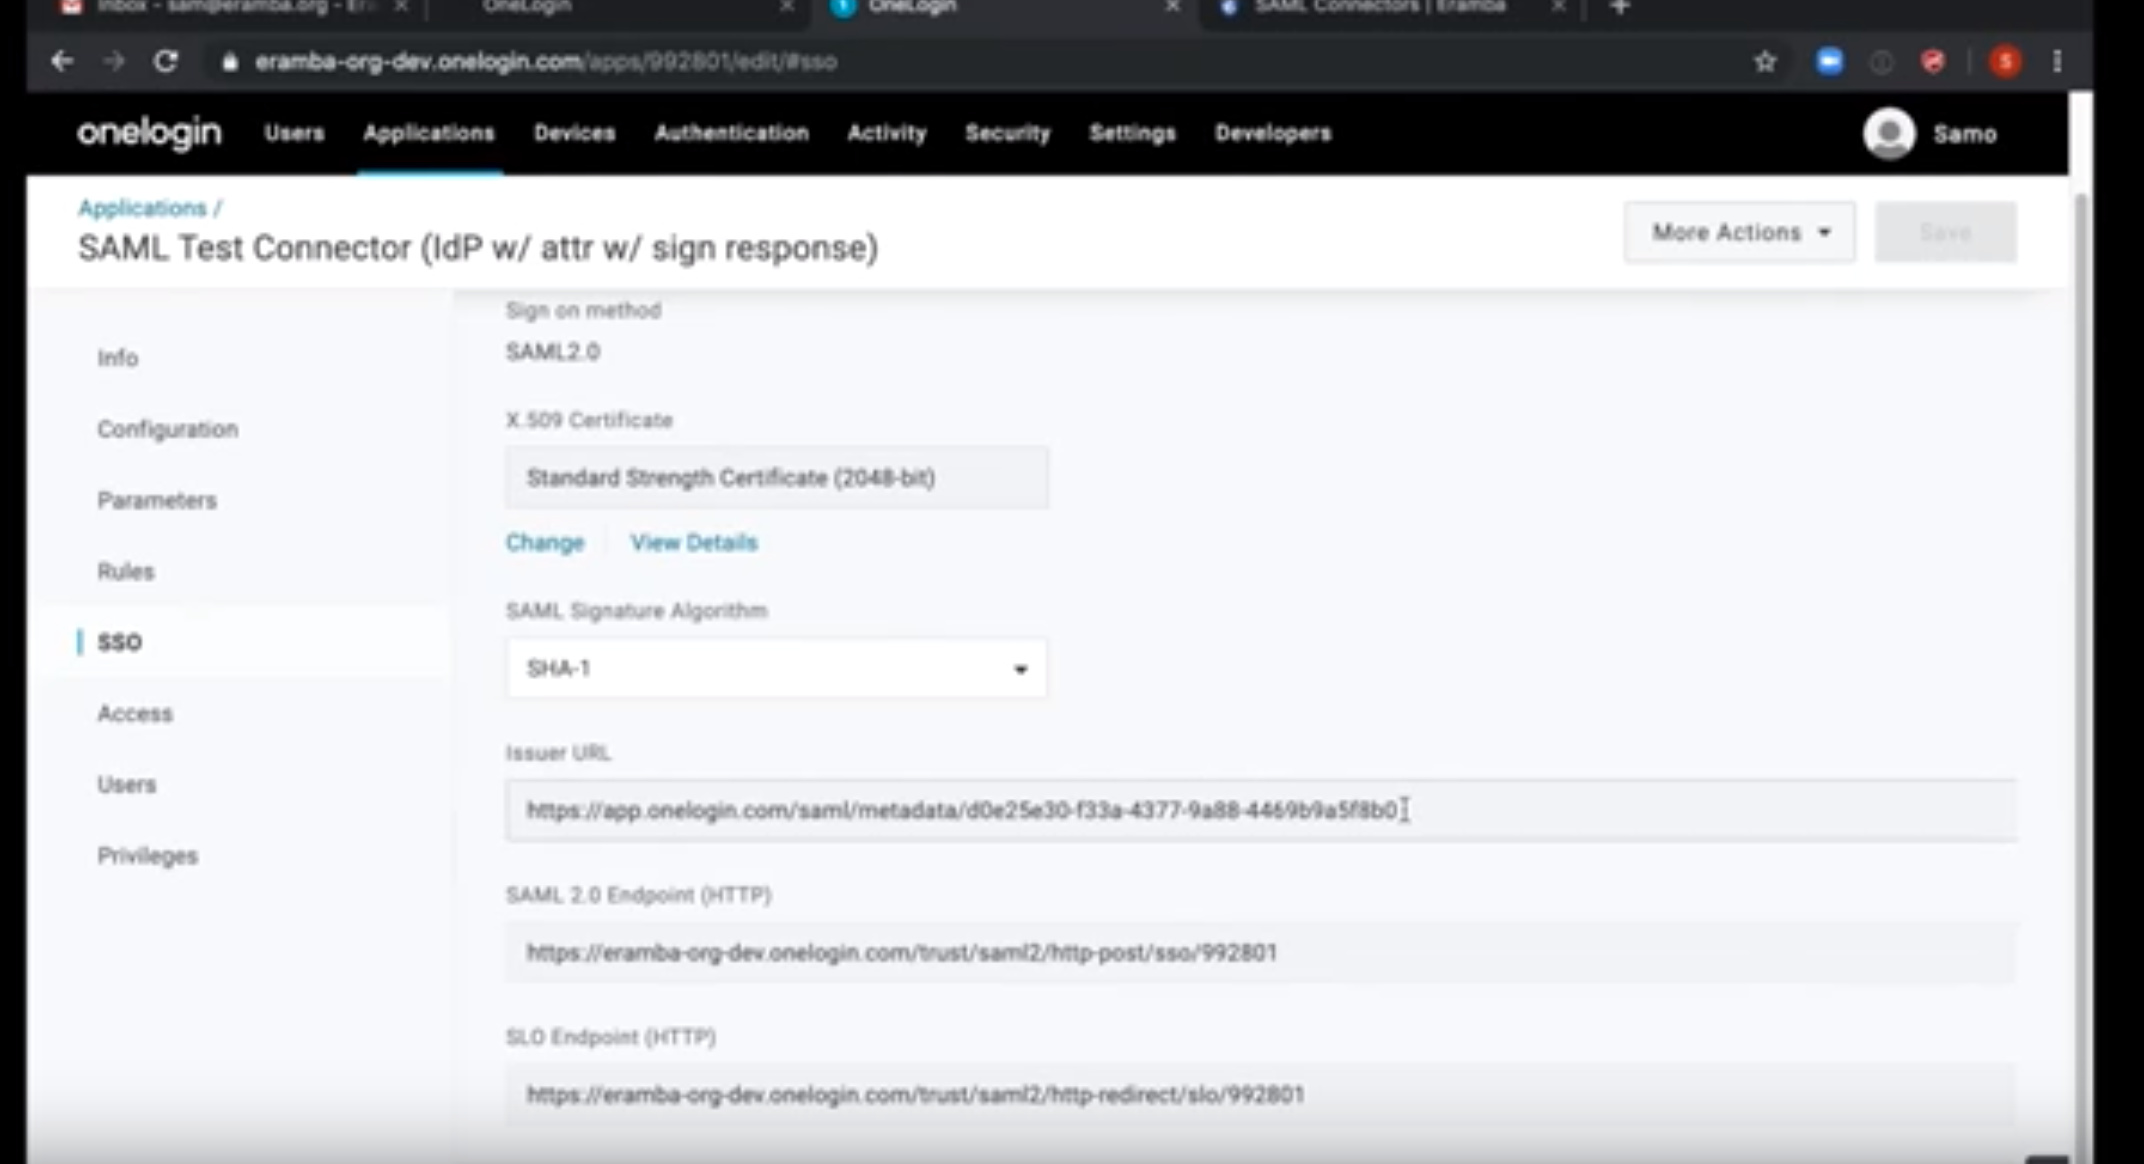
taadaaaaa, SAML finally seems to work and will be part of release 2.7.0 (due for this week or next monday)
video: [https://youtu.be/0mRkqTg0aR0](https://youtu.be/0mRkqTg0aR0)
THIS IS BETA!!! meaning, it should work but we are sure there will be updates.
[](https://www.youtube.com/watch?v=0mRkqTg0aR0)
[Next page](https://discussions.eramba.org/t/feature-saml-planned-for-r46/494.md?page=2)